
EPISODE · Sep 3, 2026 · 28 MIN
1532-Foundations of LLM Safety and Security in Healthcare
from Paper Talk
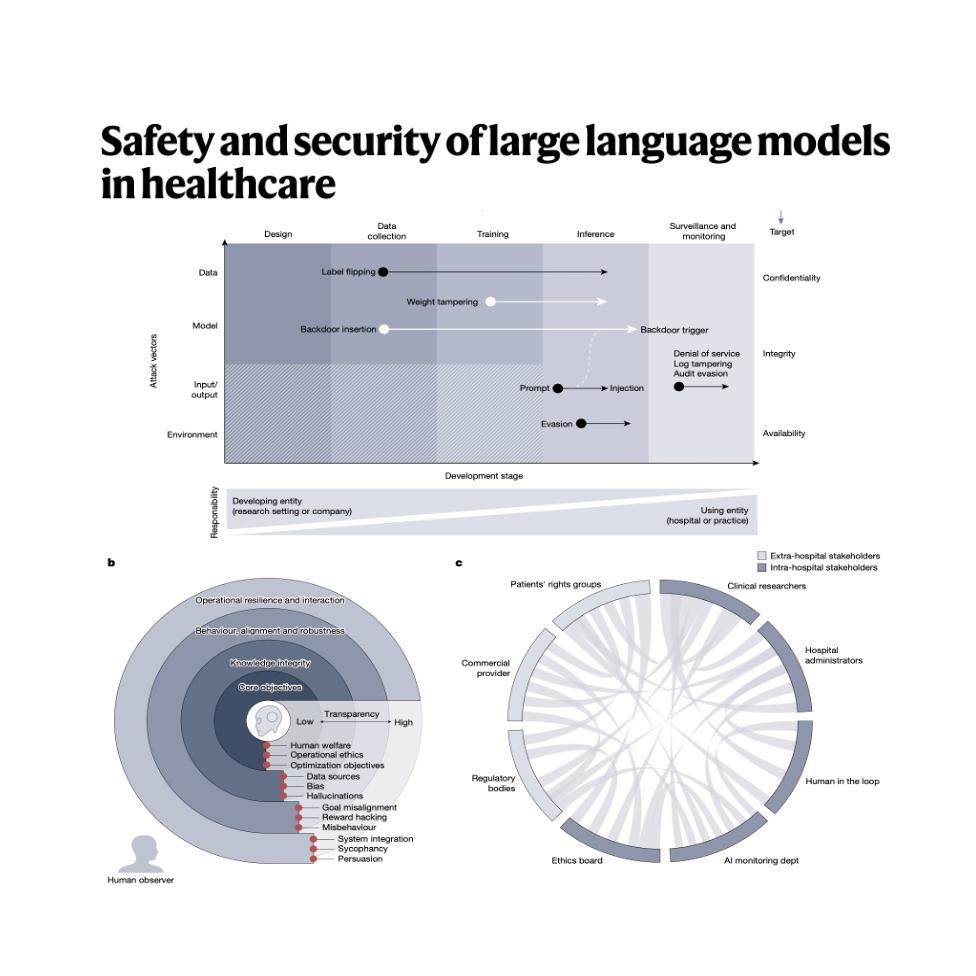
Recent advances in generative artificial intelligence have introduced large language models (LLMs) into various medical fields, promising to enhance clinical documentation and decision support. Despite these benefits, the integration of these models into healthcare systems creates significant safety and security vulnerabilities that require urgent attention. Malicious actors may exploit these systems through adversarial attacks, such as data poisoning or prompt injections, to compromise patient confidentiality and treatment integrity. Additionally, inherent risks like hallucinations, algorithmic bias, and automation bias can lead to incorrect medical advice if not properly managed. To address these threats, the sources propose a multi-layered framework involving continuous monitoring, rigorous auditing, and clear regulatory oversight. Ultimately, establishing trustworthy AI in medicine depends on a collaborative effort between developers, healthcare providers, and policymakers to ensure patient welfare remains the primary priority.References:Clusmann J, Freyer O, Ostermann M, et al. Safety and security of large language models in healthcare[J]. Nature, 2026, 656(8128): 577-589.前往小宇宙评论区与主播互动
Embed this episode
Ready to play
1532-Foundations of LLM Safety and Security in Healthcare
No transcript for this episode yet
Similar Episodes
No similar episodes found.
Similar Podcasts
No similar podcasts found.