
EPISODE · Sep 3, 2026 · 27 MIN
1532-医疗大语言模型的安全与防护综述
from 聊聊Sci
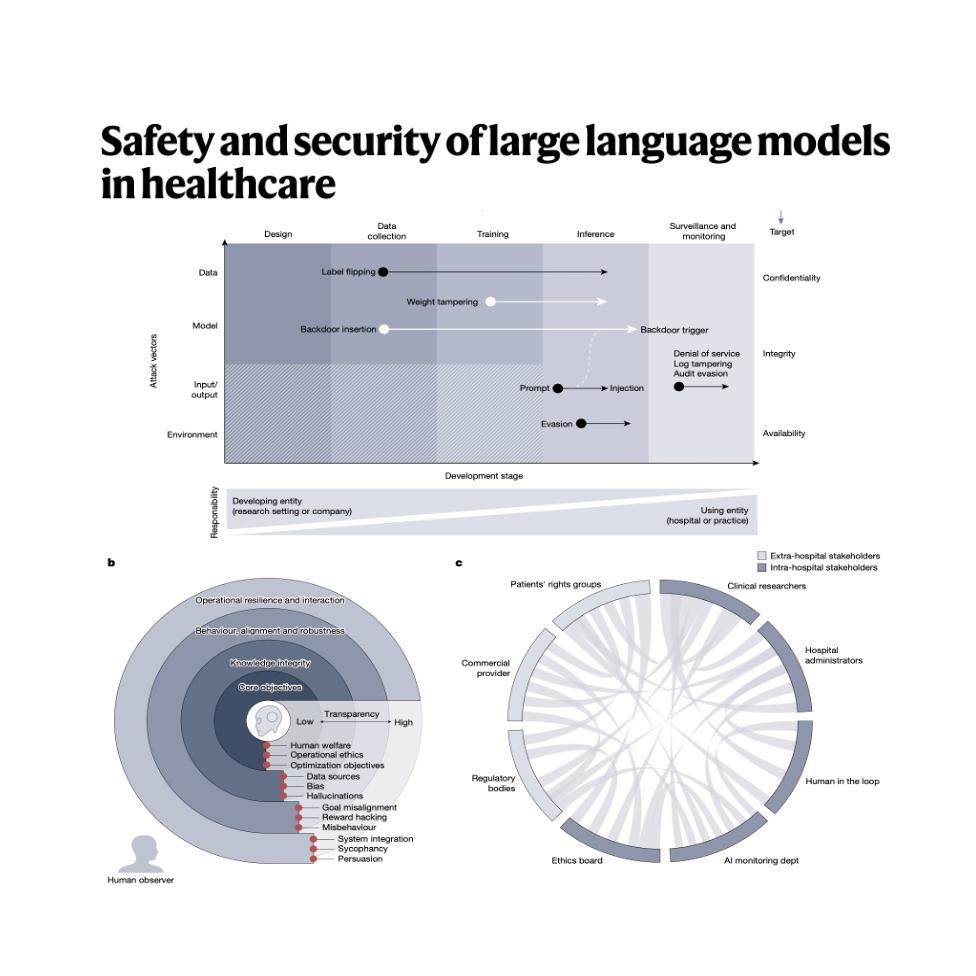
这篇文章深入探讨了大语言模型(LLM)集成到医疗体系时所面临的安全与防御挑战。作者系统性地梳理了从模型设计、数据训练到临床部署各阶段可能遭遇的恶意攻击,如提示词注入和数据投毒。除了外部威胁,研究还分析了模型固有的风险,包括幻觉、偏见以及与人类价值观失调等问题。为了确保医疗AI的可靠性,文中提议建立一套多方协作的监管框架,涵盖技术层面的加固和医院内部的持续审计。最终,文章强调在追求医疗自动化的同时,必须平衡技术创新与患者安全。References:Clusmann J, Freyer O, Ostermann M, et al. Safety and security of large language models in healthcare[J]. Nature, 2026, 656(8128): 577-589.前往小宇宙评论区与主播互动
Embed this episode
Ready to play
1532-医疗大语言模型的安全与防护综述
0:00
27:25
1×
No transcript for this episode yet
Similar Episodes
No similar episodes found.
Similar Podcasts
Forfeiture Book Review: Ecocide and Sci-Fi
JP et al.
A whizz bang review of the complex themes in the new ecological Sci-Fi novel, FORFEITURE by JP Nebra
Deep Dream State
Neural Nets And Pretty Patterns
Deep Dream State is a full-cast dystopian sci-fi and desire horror audio drama by Neural Nets and Pretty Patterns. As the originating work of desire horror, it locates the uncanny inside wanting itself. While conventional horror positions you against a threat, desire horror implicates you in it. The horror emerges from recognition: the realization of why characters stay, and why surrender feels like relief. Since 2017, the show has used research in dream science, surveillance studies, behavioral economics, and advertising technology to examine systems of control through immersive sound design and full-cast performance.
Frequently Asked Questions
How long is this episode of 聊聊Sci?
This episode is 27 minutes long.
When was this 聊聊Sci episode published?
This episode was published on September 3, 2026.
Can I download this 聊聊Sci episode?
Yes. Use the download control on the episode player to save the publisher-provided media file.
URL copied to clipboard!