
EPISODE · May 25, 2019 · 44 MIN
Æ-DIR -- Authorized Entitites Directory (osc19)
from Chaos Computer Club - archive feed (high quality) · host stroeder
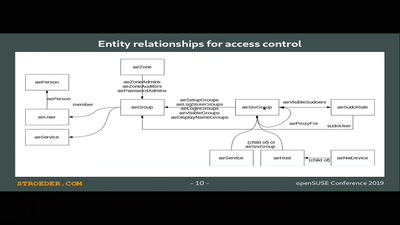
This talk will present a concept and real-world implementation of an identity and access management system (IAM) purely based on OpenLDAP. The main goal of Æ-DIR (besides challenging Unicode handling in various software with its name) is to follow the delegation, need-to-know and least-privilege principles as strictly as possible. The visibility of user, group, sudoers, etc. is limited by OpenLDAP’s set-based ACLs. All systems and services, no exception(!), have to individually authenticate to be authorized to access Æ-DIR. The talk will give some additional information about the secure base configuration of OpenLDAP and a special NSS/PAM caching demon developed for lower resource usage. This talk will present a concept and real-world implementation of an identity and access management system (IAM) purely based on OpenLDAP. The main goal of Æ-DIR (besides challenging Unicode handling in various software with its name) is to follow the delegation, need-to-know and least-privilege principles as strictly as possible. The visibility of user, group, sudoers, etc. is limited by OpenLDAP’s set-based ACLs. All systems and services, no exception(!), have to individually authenticate to be authorized to access Æ-DIR. The talk will give some additional information about the secure base configuration of OpenLDAP and a special NSS/PAM caching demon developed for lower resource usage. about this event: https://c3voc.de
Embed this episode
Ready to play
Æ-DIR -- Authorized Entitites Directory (osc19)
No transcript for this episode yet
Similar Episodes
No similar episodes found.
Similar Podcasts
No similar podcasts found.