
EPISODE · Jun 27, 2026 · 19 MIN
Course 37 - Building Web Apps with Ruby On Rails | Episode 14: From Basic HTTP to JWT Authentication
from CyberCode Academy · host CyberCode Academy
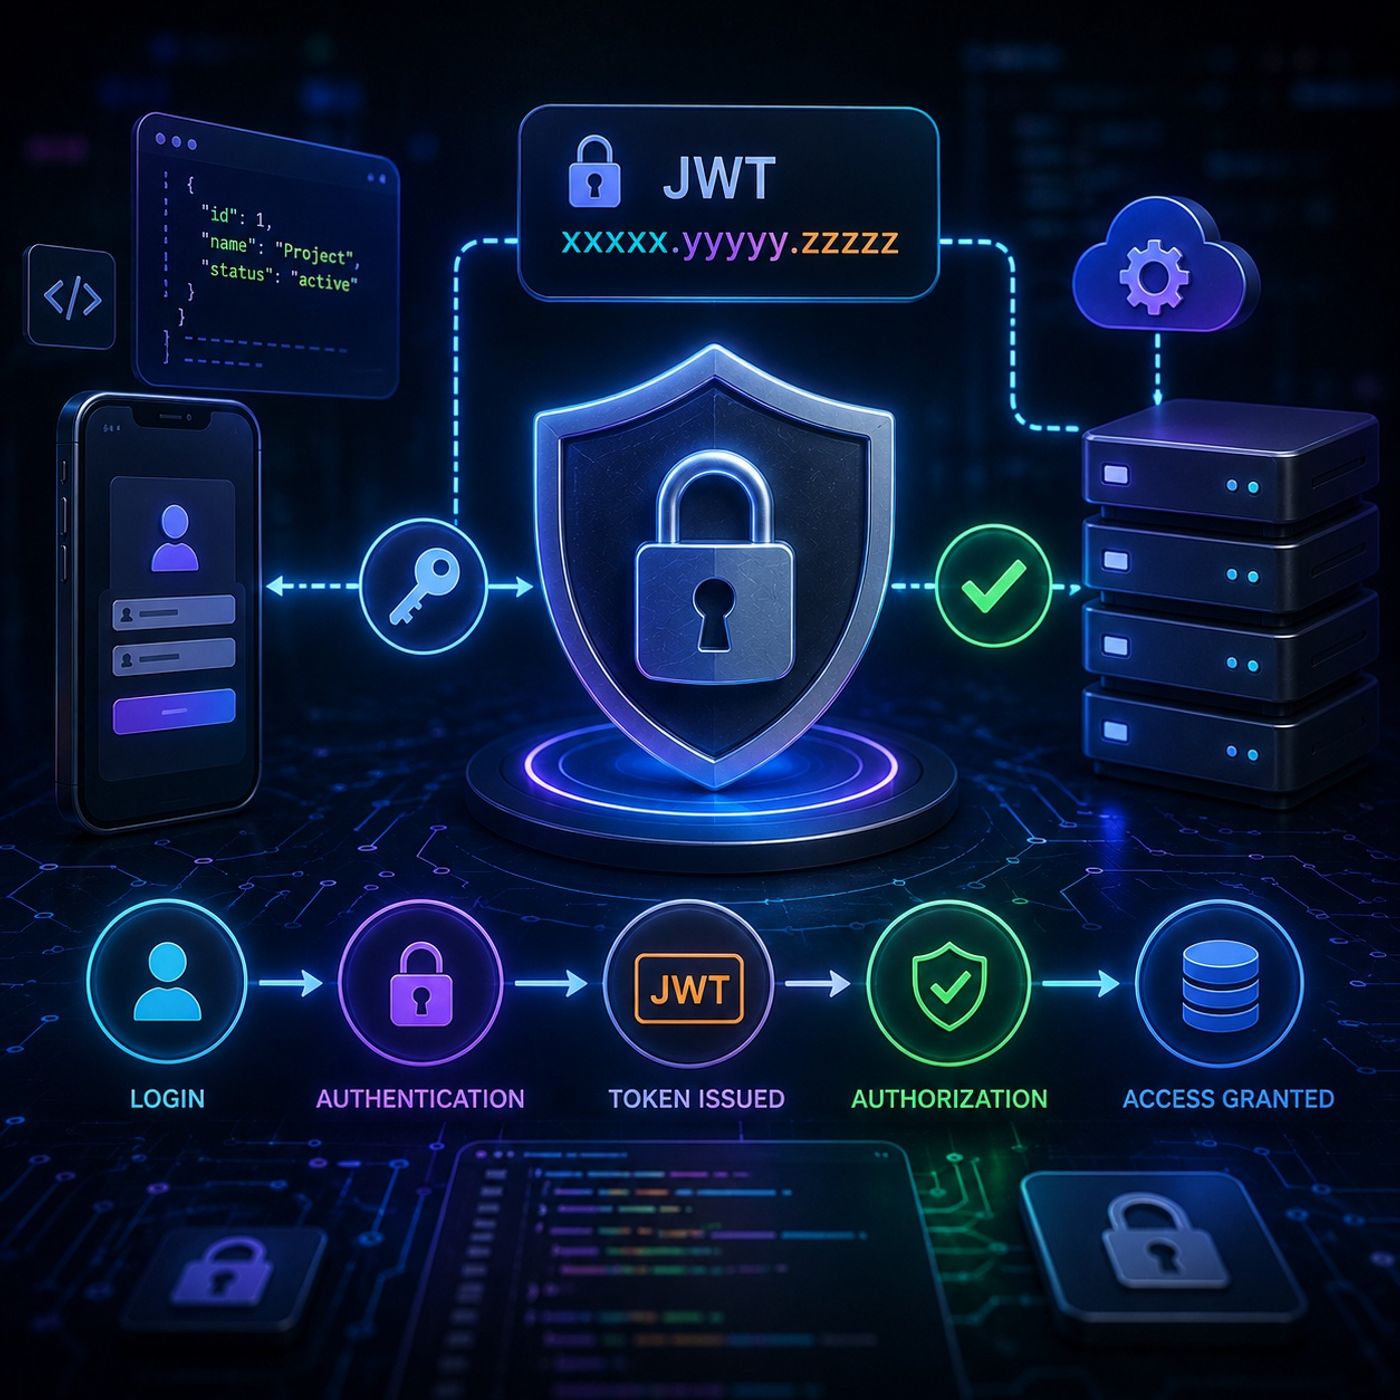
In this lesson, you’ll learn about: securing APIs in Rails, authentication strategies, and building a stateless authorization system1. Why API Security MattersUsing Ruby on Rails APIs:🔹 Problem:APIs are publicly exposed endpointsWithout protection → anyone can access or manipulate data🔹 Goal:Ensure only authorized users can interact with resources👉 Key InsightAn unsecured API is essentially a “wide-open backend”2. Foundation of API Design🔹 Core features:Multiple response formats (JSON)PaginationAPI versioning🔹 Example:/api/v1/projects?page=1 👉 Key InsightSecurity must be designed alongside API structure—not added later3. Basic HTTP Authentication (Intro Level)🔹 Rails method:http_basic_authenticate_with name: "admin", password: "secret" 🔹 How it works:Sends username/password with every request🔹 Problems:Credentials sent repeatedlyOften stored or cachedVulnerable if not encrypted👉 Key InsightGood for demos ❌Not safe for production ❌4. Token-Based Authentication with JWTUsing JSON Web Token:🔹 Structure:HeaderPayloadSignature🔹 Example:xxxxx.yyyyy.zzzzz 🔹 Benefits:Stateless (no server session needed)Secure (signed token)Scalable👉 Key InsightJWT is the industry standard for modern APIs5. Why JWT Is More Secure🔹 Advantages:No repeated credentialsToken can expireCannot be modified without secret key🔹 Protection:Immune to CSRF (no cookies required)👉 Key InsightSecurity comes from signature verification, not secrecy6. Implementing JWT in Rails🔹 Tool:JWT Ruby Gem🔹 Encoding:JWT.encode(payload, secret_key) 🔹 Decoding:JWT.decode(token, secret_key) 👉 Key InsightThe server is the only entity that can generate valid tokens7. Authentication Service🔹 Responsibilities:Handle signupHandle loginGenerate token🔹 Flow:User logs inServer validates credentialsServer returns JWT👉 Key InsightAuthentication = verifying identity8. Authorization Layer🔹 Implementation:Add before_action in controllerbefore_action :authorize_request 🔹 Process:Extract token from headersDecode tokenIdentify current user👉 Key InsightAuthorization = controlling access9. Request Lifecycle with JWT🔹 Flow:Client sends request with tokenServer validates tokenAccess granted or denied👉 Key InsightEvery request is independently verified (stateless system)10. From Open API to Secure System🔹 Before:No identity checkFull data exposure🔹 After:Token requiredUser-specific access control👉 Key InsightSecurity transforms your API from public → protectedKey TakeawaysBasic auth is simple but insecureJWT provides stateless, scalable securitySeparate authentication and authorization logicValidate every request using tokensBig PictureYou are building:👉 A stateless authentication system👉 A scalable API architecture👉 A secure backend for mobile/web appsMental ModelUser logs in → server issues token → client stores token → sends with each request → server verifies → grants/denies accessYou can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
Ready to play
Course 37 - Building Web Apps with Ruby On Rails | Episode 14: From Basic HTTP to JWT Authentication
No transcript for this episode yet
Similar Episodes
No similar episodes found.