
EPISODE · Jul 3, 2026 · 23 MIN
Course 38 - Web Security Known Web Attacks | Episode 2: RCE Filter Bypassing and JSON Hijacking
from CyberCode Academy · host CyberCode Academy
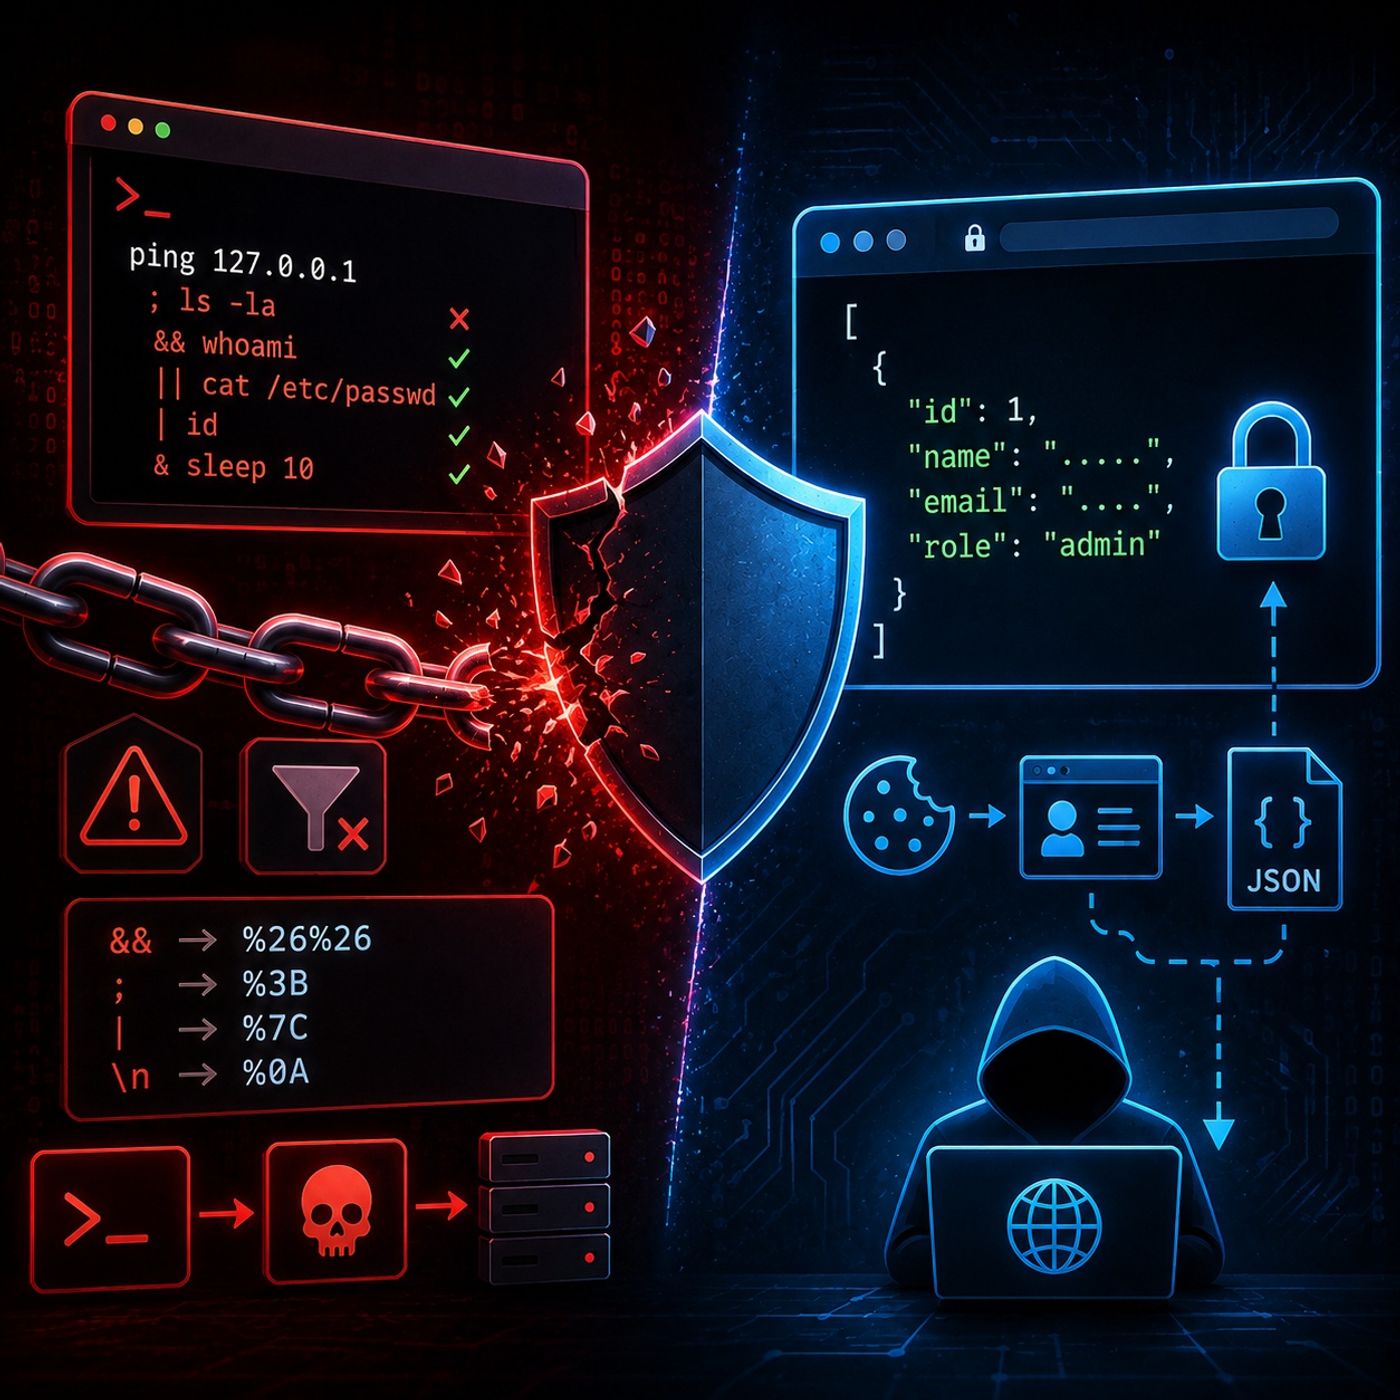
In this lesson, you’ll learn about: bypassing weak RCE filters and understanding JSON hijacking (legacy browser vulnerability)1. Why RCE Filters Fail🔹 Common mistake:Developers block specific characters (like ;)🔹 Problem:Attack surface is much larger than one delimiter👉 Key InsightBlacklisting single characters is not real security2. Alternative Command Operators🔹 Even if ; is blocked, others exist:&& → execute if first succeeds|| → execute if first fails| → pipe output& → background execution👉 Key InsightThere are multiple ways to chain commands, not just one3. Encoding to Bypass Filters🔹 Web applications often filter raw characters🔹 Bypass technique:Use URL encoding🔹 Example:&& → %26%26👉 Key InsightFilters that don’t normalize input can be bypassed easily4. Logic-Based Exploitation🔹 Operator behavior matters:&& → requires success|| → requires failure🔹 Attacker strategy:Force first command to fail → trigger second👉 Key InsightExploitation is about logic control, not just syntax5. Core Defense Principle🔹 Problem:Input filtering ≠ protection🔹 Real solution:Never pass user input to system commands👉 Key InsightEliminate the sink, not just sanitize input6. What is JSON Hijacking🔹 Definition:A client-side data theft attack exploiting browser behavior🔹 Related concept:Similar to Cross-Site Request Forgery (CSRF)👉 Key InsightIt abuses authenticated requests + weak browser protections7. How JSON Hijacking Works (Conceptually)🔹 Key idea:🔹 Attack flow:Victim is logged inAttacker loads sensitive API via Browser sends cookies automaticallyData is exposed to attacker-controlled logic👉 Key InsightSame-Origin Policy historically did not fully protect script loading8. The Role of JavaScript InternalsUsing JavaScript:🔹 Technique:Override object behavior (e.g., setters)Intercept sensitive values during parsing👉 Key InsightAttackers abused how JavaScript handled object properties9. Why JSON Hijacking Worked (Historically)🔹 Root causes:Weak SOP enforcement for scriptsBrowsers executing JSON as JavaScriptSensitive data returned as raw JSON arrays👉 Key InsightIt was a browser + API design flaw combination10. Why It’s Mostly Fixed Today🔹 Modern protections:Strict Same-Origin PolicyCORS enforcementJSON responses require proper headersSafer browser engines👉 Key InsightThis is now mostly a legacy vulnerability11. How to Prevent JSON Hijacking🔹 Best practices:Use proper Content-Type: application/jsonAvoid returning raw arrays (wrap in objects)Require authentication headers (not just cookies)Implement CSRF protections👉 Key InsightModern API design prevents this class of attack12. Big Security Lessons🔹 From RCE:Never trust user inputAvoid system command execution🔹 From JSON Hijacking:Don’t rely on browser behaviorAlways enforce server-side protections👉 Key InsightSecurity failures often come from incorrect assumptionsKey TakeawaysRCE filters are easily bypassed with alternative operators and encodingLogical execution flow is key to exploitationJSON hijacking exploited legacy browser behaviorModern defenses have largely mitigated itSecure design > reactive filteringBig PictureYou are learning:👉 How attackers bypass naive defenses👉 How browser and server interactions can be abused👉 How modern security practices evolved from past vulnerabilitiesMental ModelWeak filter → bypass → command executionWeak browser policy → data exposure → session abuseYou can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
Ready to play
Course 38 - Web Security Known Web Attacks | Episode 2: RCE Filter Bypassing and JSON Hijacking
No transcript for this episode yet
Similar Episodes
No similar episodes found.