
EPISODE · Jul 8, 2026 · 21 MIN
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 2: Mitigating RCE, OS Injection, and Path Traversal Vulnerabilities
from CyberCode Academy · host CyberCode Academy
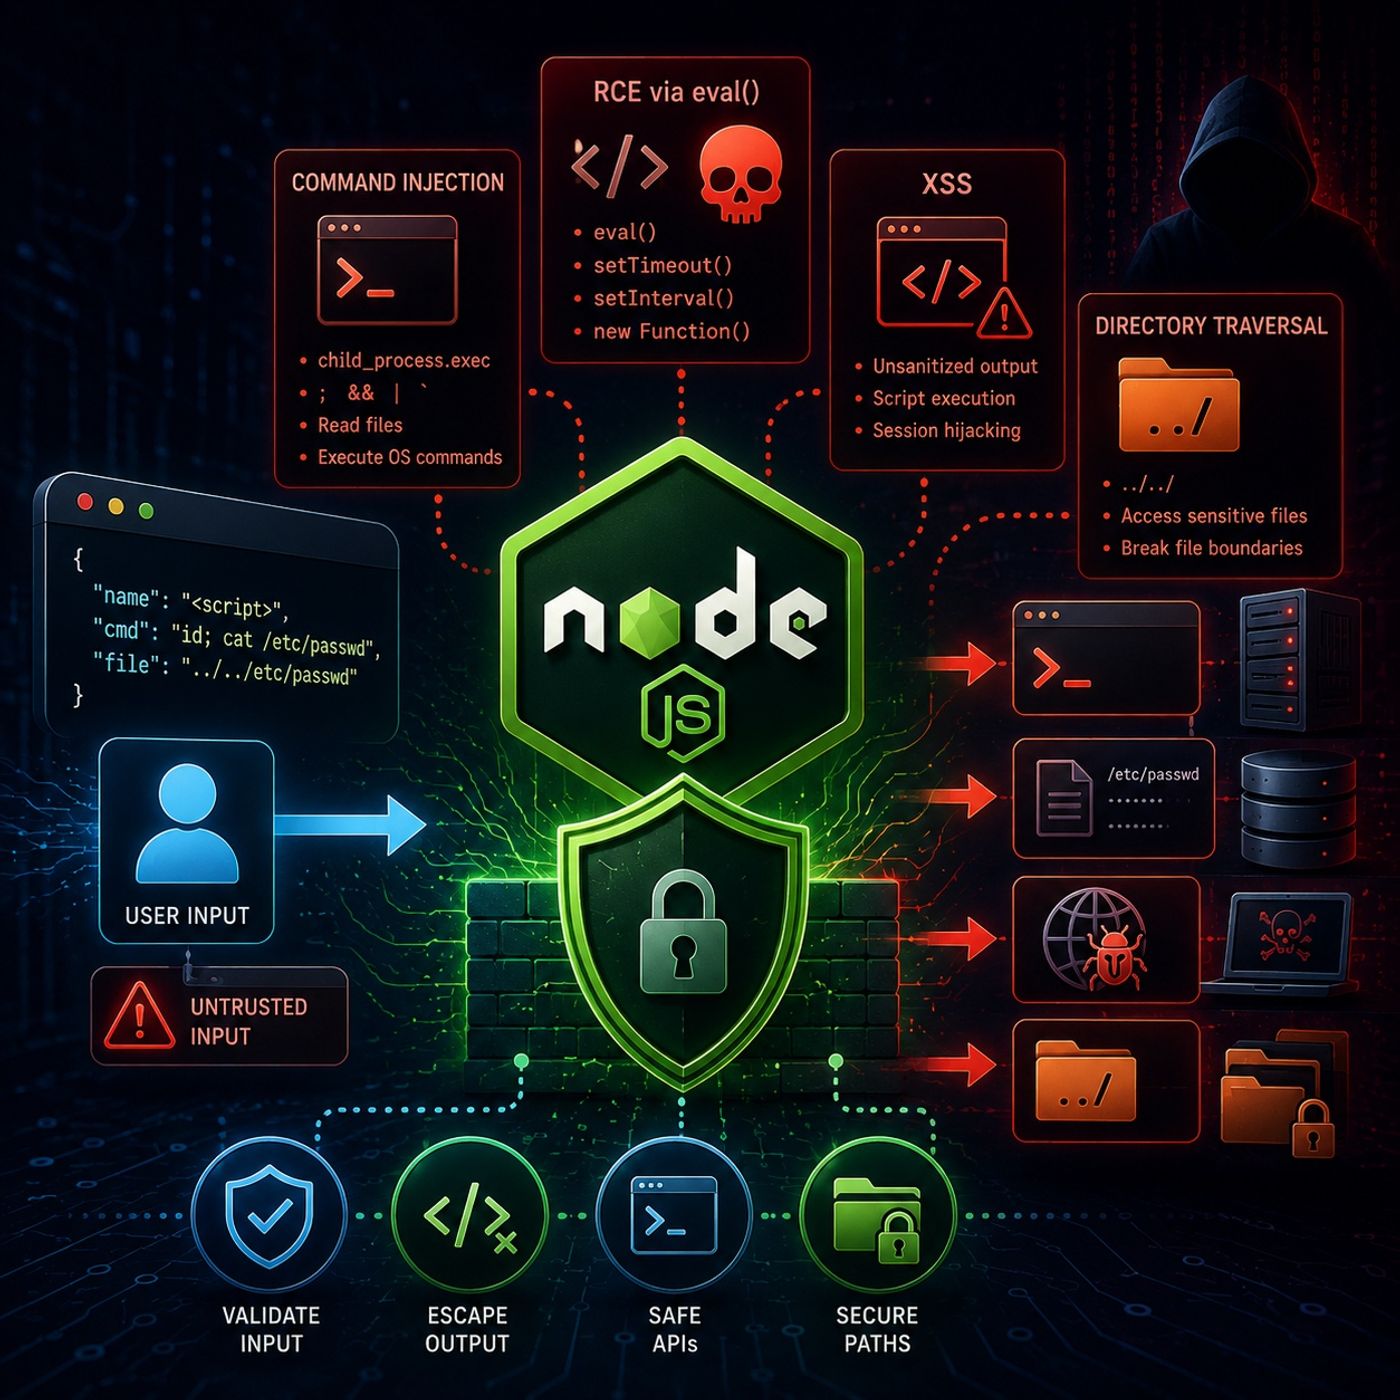
In this lesson, you’ll learn about: critical Node.js vulnerabilities caused by unsafe user input handling, including RCE, command injection, XSS, and directory traversal1. Core Security Principle🔹 Key idea:Never trust user input👉 Any data from users must be treated as hostile by defaultWithout validation, it can become a direct execution path into the system.2. Remote Code Execution (RCE) via eval()🔹 Dangerous functions:eval()setTimeout()setInterval()new Function()🔹 Why they are riskyThese functions execute raw JavaScript strings🔹 Attack outcomes:Infinite loops → server crash (DoS)Forced termination (process.exit())Full server takeover (reverse shell execution)👉 Key InsightIf user input reaches an execution function → the server is effectively “remote-controlled”3. Remote OS Command Injection🔹 Vulnerable function:child_process.exec🔹 How the attack works:Input is passed into shell commandsAttacker injects separators like ;Extra commands execute on the OS🔹 Example impact:Read sensitive files (e.g., system password data)Execute arbitrary system commands🔹 Safer alternatives:execFilespawn👉 Why they are safer:They treat input as arguments, not executable shell strings4. Cross-Site Scripting (XSS)🔹 Cause:Unsanitized user input reflected into browser output🔹 Impact:Script execution in victim’s browserSession hijacking potentialUI manipulation👉 Key InsightServer-side mistake becomes client-side compromise5. Directory Traversal (Path Traversal)🔹 Technique:Using patterns like:../repeated directory jumps🔹 Impact:Access files outside intended directoryRead sensitive system filesBreak application file boundaries6. Big PictureThis episode shows how Node.js apps fail when:Input is executed instead of validatedSystem commands are built from raw stringsOutput is rendered without escapingFile paths are not restrictedMental ModelUser input → execution boundary → system accessIf that chain is not broken at validation → full compromise becomes possibleYou can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
Ready to play
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 2: Mitigating RCE, OS Injection, and Path Traversal Vulnerabilities
No transcript for this episode yet
Similar Episodes
No similar episodes found.