
EPISODE · Jul 9, 2026 · 19 MIN
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 3: Hardening Code and Preventing Attacks
from CyberCode Academy · host CyberCode Academy
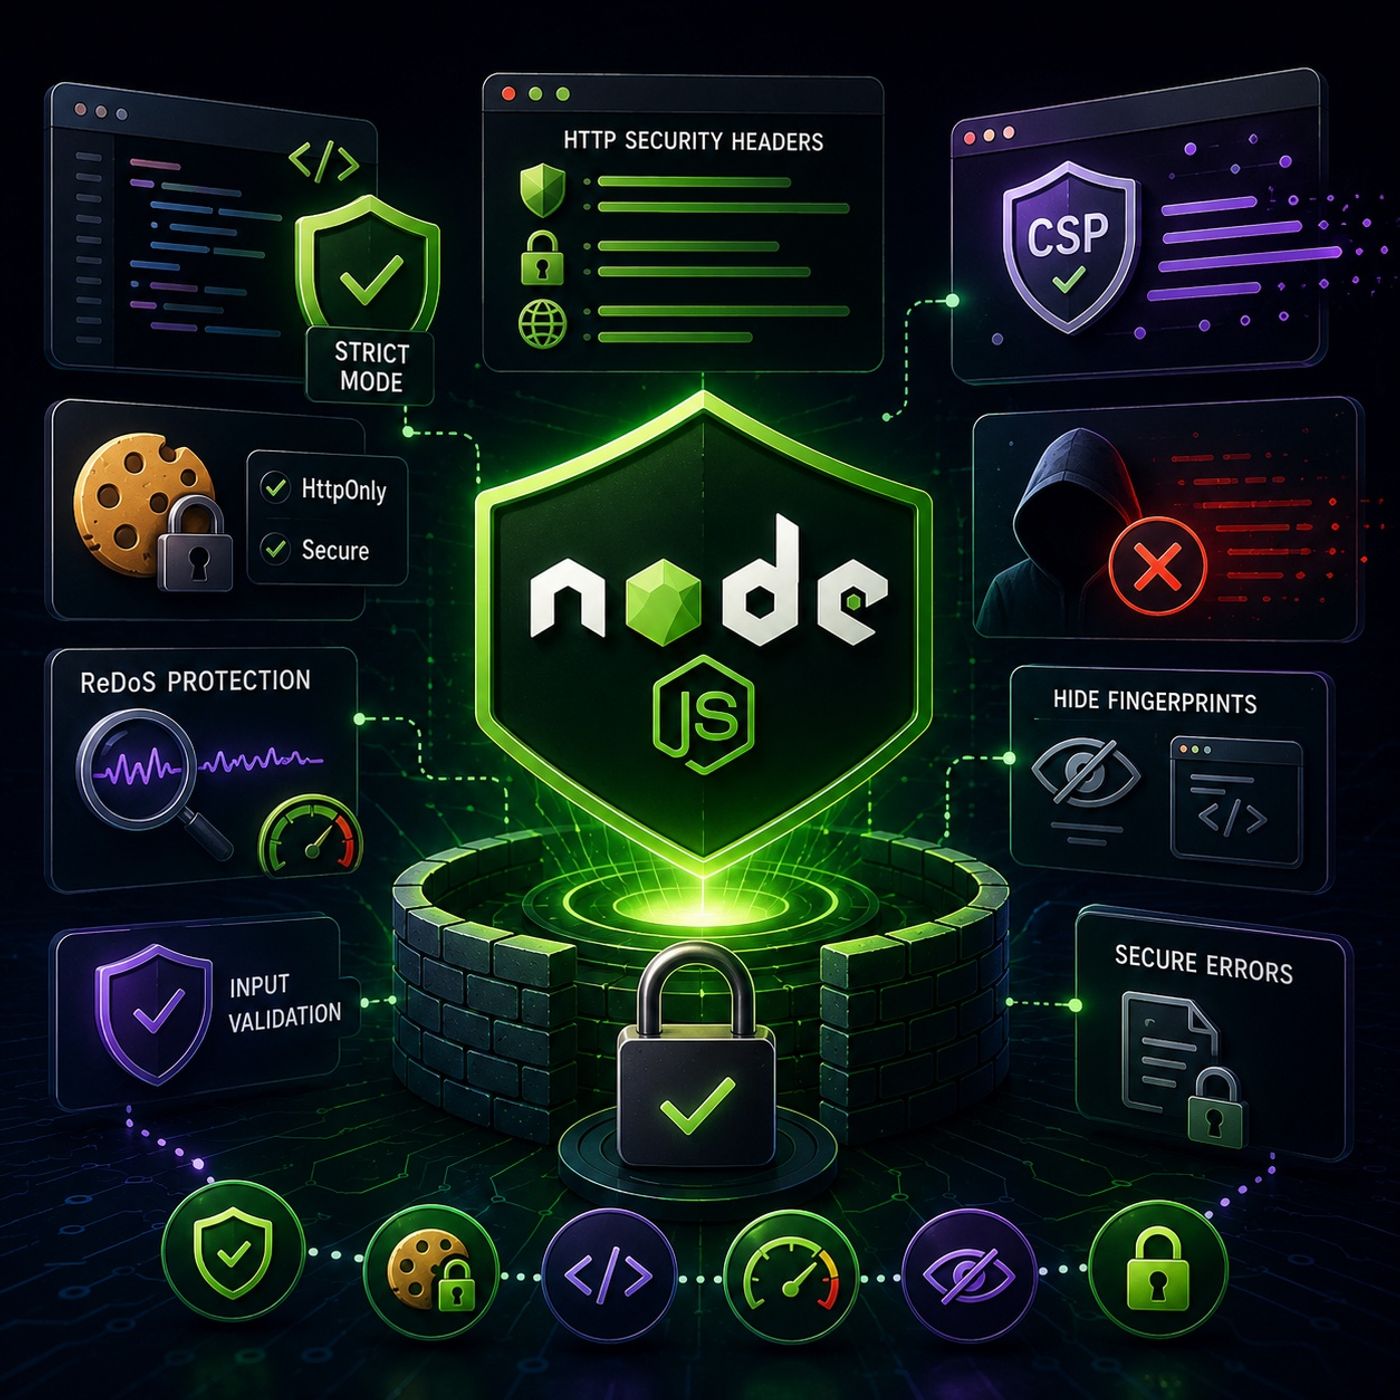
In this lesson, you’ll learn about: securing Node.js applications through safe coding practices, HTTP security headers, ReDoS protection, and preventing information disclosure1. Secure Coding in Node.js🔹 Key idea:Secure Node.js applications require strict control over execution context and defaults.🔹 Strict ModeEnables safer JavaScript executionPrevents accidental global variablesForces explicit variable declarations👉 Key InsightStrict mode reduces “silent” security bugs caused by sloppy scope handling2. HTTP Security Headers (Defense Layer)🔹 Tool:Helmet.js🔹 What it does:Automatically sets important security headers in Express apps.🔹 Key headers it manages:Content Security Policy (CSP) → blocks malicious scriptsHTTP Strict Transport Security (HSTS) → forces HTTPSXSS Protection headers → reduces injection risks👉 Key InsightHeaders act as a browser-level security shield3. Secure Cookies🔹 Important flags:HttpOnlyBlocks JavaScript access to cookiesSecureEnsures cookies are only sent over HTTPS👉 Key InsightEven if XSS happens, HttpOnly cookies cannot be stolen via JS4. Regular Expression Denial of Service (ReDoS)🔹 What it is:A performance attack exploiting bad regex patterns🔹 How it works:Complex input causes exponential backtrackingCPU usage spikesServer becomes unresponsive🔹 Common risk area:Email validationInput sanitization👉 Key InsightA “valid” input can still be a computational attack5. Preventing ReDoS Attacks🔹 Strategies:Avoid overly complex regex patternsLimit input lengthUse safe validation librariesBenchmark regex performance👉 Key InsightSecurity includes performance safety, not just access control6. Information Disclosure Risks🔹 Problem:Attackers learn stack/framework details from responses7. Hiding Technology Fingerprints🔹 Disable default headersRemove X-Powered-ByHide framework identity🔹 Tools:Express.jsExample:Default headers reveal backend technologyRemoving them reduces attack surface visibility8. Session Cookie Hardening🔹 Risk:Default cookies like connect.sid reveal framework usage🔹 Fix:Rename cookiesCustomize session identifiers👉 Key InsightSmall naming details can expose backend stack9. Custom Error Handling🔹 Problem:Default errors expose:Stack tracesFile pathsInternal logic🔹 Fix:Use production-safe error handlersReturn generic messages only👉 Key InsightErrors should help users—not attackers10. Big PictureYou are learning how to:👉 Harden Node.js applications at multiple layers👉 Prevent CPU-based DoS attacks (ReDoS)👉 Reduce information leakage from HTTP responses👉 Apply production-grade security middlewareMental ModelStrict mode → secure headers → safe cookies → regex safety → hidden fingerprints → controlled errors → hardened application surfaceYou can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
Ready to play
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 3: Hardening Code and Preventing Attacks
No transcript for this episode yet
Similar Episodes
No similar episodes found.