
EPISODE · Jul 10, 2026 · 24 MIN
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 4: Manual and Automated Code Review Essentials
from CyberCode Academy · host CyberCode Academy
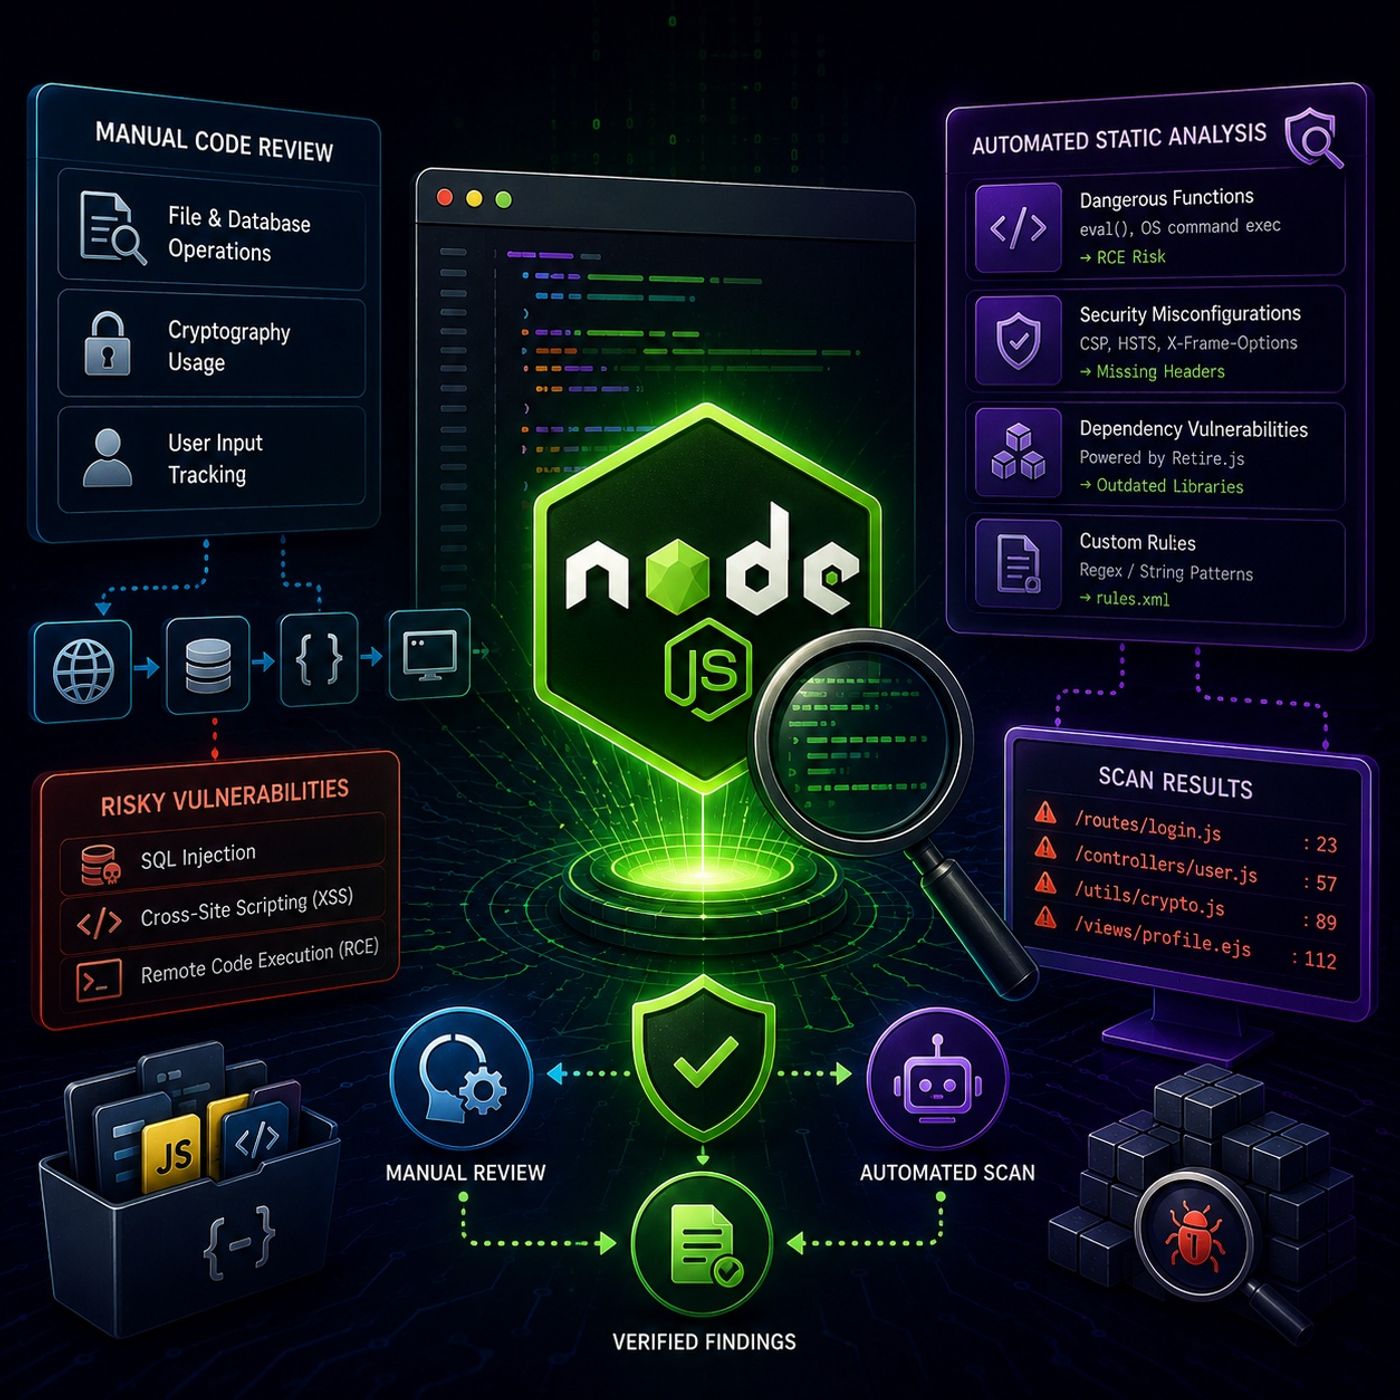
In this lesson, you’ll learn about: auditing Node.js applications using manual code review techniques and automated static analysis tools to identify security vulnerabilities1. What is Node.js Application Auditing?🔹 Purpose:Systematically review a Node.js codebase to find security weaknesses before attackers do🔹 Two main approaches:Manual code reviewAutomated static analysis👉 Key ideaReal security comes from combining both approaches2. Manual Code Review Strategy🔹 Focus areas during review:🔹 File and database operationsLook for unsafe reads/writesCheck uncontrolled file paths🔹 Cryptography usageWeak hashing (e.g., MD5)Disabled SSL verificationImproper encryption handling🔹 User input trackingFollow input from:request → processing → database → response👉 Key InsightMost vulnerabilities appear where input is not properly encoded or escaped🔹 Common resulting vulnerabilities:SQL InjectionCross-Site Scripting (XSS)Remote Code Execution (RCE)🔹 Reference knowledge base:OWASP Code Review Guide3. Automated Static Analysis (NodeJsScan)🔹 Tool:NodeJsScan🔹 What it does:Scans code without running it to detect security issues🔹 Key detection capabilities:1. Dangerous functionseval()OS command execution functions👉 Flags potential RCE paths2. Security misconfigurationsMissing CSP headersMissing HSTSMissing X-Frame-Options3. Dependency vulnerabilitiesUses Retire.jsDetects outdated or vulnerable libraries4. Custom rule supportAdd regex/string patternsConfigure rules in rules.xml4. Practical Workflow ExampleUsing vulnerable apps like NodeGoat:Tool scans entire codebaseFlags vulnerable linesShows file + exact line numberSpeeds up remediation process5. Big PictureSecurity auditing is about:Manual review → deep understandingStatic analysis → fast detection at scale👉 Best practice:Use both together for complete coverageMental ModelCode → input flow tracking → unsafe sinks → automated scanning → verified findingsYou can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
Ready to play
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 4: Manual and Automated Code Review Essentials
No transcript for this episode yet
Similar Episodes
No similar episodes found.