
EPISODE · Aug 30, 2026 · 15 MIN
Course 42 - Mobile Malware Analysis Fundamentals | Episode 3: iOS Application Architecture and Jailbreaking Fundamentals
from CyberCode Academy · host CyberCode Academy
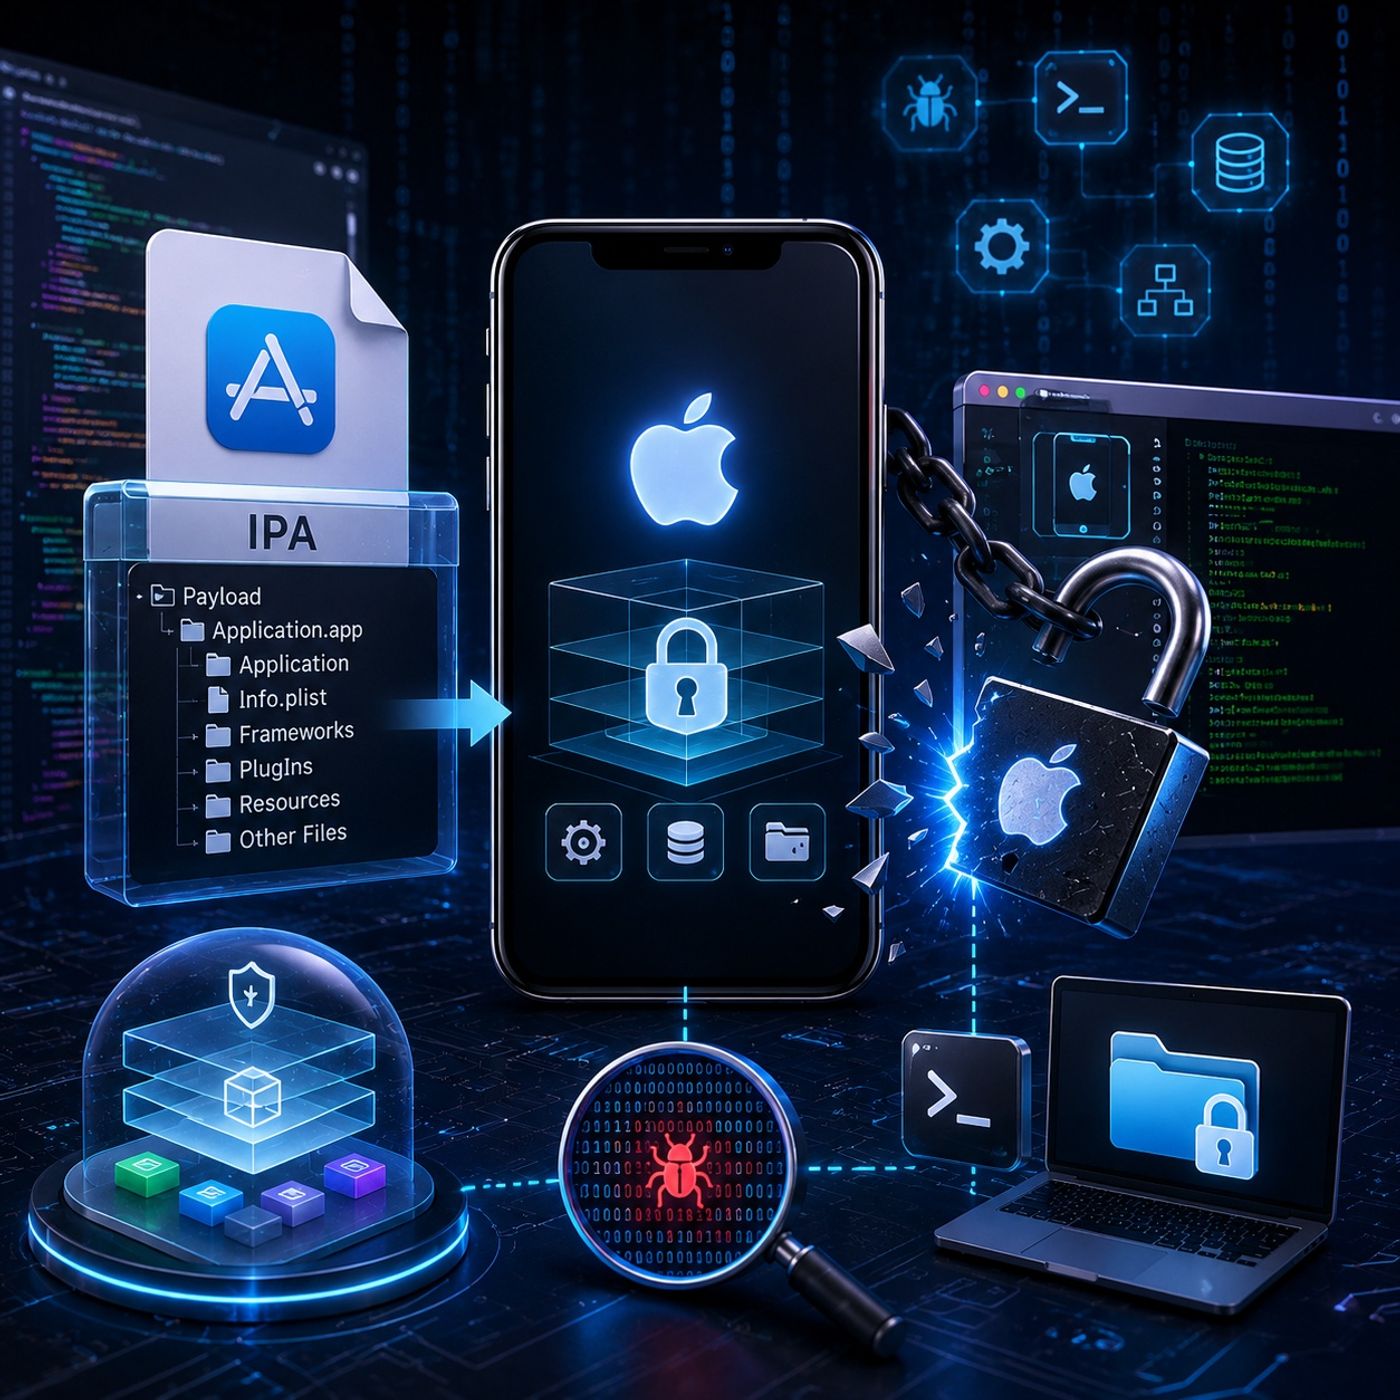
iOS Application Architecture & Jailbreaking — Advanced Study Template1. iOS Application ArchitectureiOS applications are primarily developed using:SwiftObjective-CXcode as the main development environmentAfter compilation, an application is packaged into an IPA (iOS App Store Package).An IPA is essentially an archive containing the components required to install and execute the application.2. Anatomy of an IPAA typical IPA contains a structure similar to:Application.ipa │ └── Payload/ │ └── Application.app/ ├── Application ├── Info.plist ├── Frameworks/ ├── PlugIns/ ├── Resources └── Other application files Payload DirectoryThe Payload directory is particularly important during static analysis.It contains the application's .app bundle.Inside the bundle, analysts can locate:Application executableInfo.plistFrameworksResourcesEmbedded componentsConfiguration files3. Info.plistThe Info.plist file contains important application metadata and configuration information.Depending on the application, it may reveal things such as:Bundle identifierApplication versionDisplay nameSupported platformsRequired capabilitiesURL schemesPermissions-related configurationSecurity relevanceDuring static analysis, Info.plist is often one of the first files worth examining because it can provide a quick overview of how the application is configured.4. Application BinaryThe .app bundle normally contains the application's executable binary.For example:Payload/ └── Example.app/ ├── Example ├── Info.plist └── ... The binary contains the compiled application logic.Static AnalysisA basic static-analysis workflow can therefore begin with:IPA ↓ Extract Archive ↓ Open Payload/ ↓ Identify .app Bundle ↓ Inspect Info.plist ↓ Identify Executable ↓ Analyze Binary 🔐 5. The iOS SandboxOne of the most important security mechanisms in iOS is application sandboxing.Each application operates within a restricted environment rather than having unrestricted access to the operating system.Conceptually: iOS │ ┌────────┴────────┐ │ │ App A App B │ │ Sandbox Sandbox │ │ Private Data Private Data The sandbox limits an application's ability to:Access other applications' private dataModify protected system filesInteract directly with restricted system resourcesEscape its designated environment6. Application ContainersAn application generally has separate areas for different types of data.Conceptually:Application BundleContains the application itself:ExecutableResourcesConfigurationData ContainerContains application-generated data such as:DatabasesUser preferencesCached informationApplication filesTemporary StorageUsed for temporary data that does not need permanent storage.🧪 7. Static Analysis of an IPAA basic analysis begins by extracting the IPA.Conceptually:Application.ipa ↓ Extract ↓ Payload/ ↓ Application.app/ ↓ ┌───────────────┐ │ Info.plist │ │ Executable │ │ Frameworks │ │ Resources │ └───────────────┘ The objective at this stage is to understand:What the application containsWhat executable it usesWhat configuration it declaresWhat frameworks and resources are bundled🔓 8. What Is Jailbreaking?Jailbreaking is the process of circumventing Apple's software restrictions to obtain greater control over an iOS device.A jailbroken device may allow researchers to:Execute software outside normal restrictionsAccess normally protected areas of the filesystemPerform deeper application analysisInstrument applicationsInject code or scriptsAccess additional debugging capabilitiesSecurity perspectiveNormal iOS:Application ↓ Sandbox ↓ Restricted APIs ↓ Protected OS Jailbroken research environment:Research Tool ↓ Elevated Access ↓ System Components ↓ Filesystem / Processes 9. How Jailbreaks WorkJailbreak techniques depend on vulnerabilities in different layers of the platform.Potential targets include:Boot ROMBootloaderKernelOther privileged system componentsThe basic concept is:Vulnerability ↓ Security Boundary Bypass ↓ Code Execution / Privilege Escalation ↓ Expanded System Access Apple continuously patches vulnerabilities used by jailbreaks, so jailbreak compatibility is highly dependent on the specific device and iOS version.10. Types of JailbreaksTethered JailbreakA tethered jailbreak generally requires assistance from another computer after the device reboots.Without the required boot process, the device may not boot normally.Semi-Untethered JailbreakThe device can generally boot normally, but the jailbreak functionality must be reactivated after certain reboots.Untethered JailbreakThe jailbreak remains active across reboots without requiring external assistance.This is historically the most persistent form.11. Jailbreaking for Security ResearchFor mobile malware researchers, jailbreaking can provide capabilities unavailable on a standard device.It can make it possible to:Inspect protected filesystem areas/ ├── System ├── Applications ├── Library ├── Private data └── Other protected areas Inspect processesResearchers can investigate:Running processesProcess relationshipsLoaded componentsApplication behaviorInstrument applicationsResearchers can use instrumentation techniques to observe or modify application behavior during execution.12. Cydia and Research ToolingHistorically, Cydia has been an important package-management environment within the jailbroken iOS ecosystem.It can provide access to packages and research utilities that are unavailable on a standard device.In the demonstrated environment, Cydia is used as part of establishing a research-oriented jailbroken setup.13. SSH AccessOnce an appropriate research environment is established, SSH can provide remote command-line access to the device.Conceptually:Analysis Computer │ │ SSH ▼ Jailbroken iOS Device │ ▼ Elevated Shell │ ▼ Filesystem / Processes This is particularly useful for security researchers because it allows them to perform analysis without relying exclusively on the normal iOS user interface.14. Why Jailbreaking Matters to Malware AnalysisWithout elevated access, researchers may encounter significant visibility limitations.A normal device enforces:SandboxingCode-signing restrictionsFilesystem protectionsProcess isolationRestricted system APIsA controlled jailbroken research device can provide considerably greater visibility.This enables techniques such as:Runtime inspectionFilesystem examinationProcess monitoringScript injectionApplication instrumentationDeeper malware behavior analysis🔬 15. Static vs. Dynamic AnalysisThis episode establishes an important distinction.Static AnalysisDynamic AnalysisExamine IPA without executing itObserve application while runningInspect Info.plistMonitor runtime behaviorExamine executableInspect processesAnalyze frameworksObserve network activitySearch embedded resourcesInstrument applicationReverse engineer binaryMonitor filesystem changesA strong mobile malware investigation generally benefits from both approaches.🎯 Key TakeawaysiOS applications are commonly developed using Swift or Objective-C.Applications are distributed in IPA packages.The Payload directory contains the application bundle.Info.plist provides valuable application metadata.The application's executable contains its compiled logic.Sandboxing isolates applications from protected system resources and other applications.Jailbreaking removes or bypasses some of Apple's normal restrictions.Jailbreaks may exploit vulnerabilities in the Boot ROM, bootloader, or kernel.Different jailbreak types provide different levels of persistence.A controlled jailbroken device can significantly improve visibility during mobile security research.SSH can provide a useful command-line interface for authorized analysis.Static + dynamic analysis provides a much more complete picture of an application's behavior.Golden ConceptIPA analysis tells you what an iOS application contains; a controlled jailbroken environment allows you to investigate what that application actually does at runtime.You can listen and download our episodes for free on more than 10 different platforms:https://linktr.ee/cybercode_academy
Embed this episode
What this episode covers
iOS Application Architecture & Jailbreaking — Advanced Study Template1. iOS Application ArchitectureiOS applications are primarily developed using: Swift Objective-C Xcode as the main development environment After compilation, an application is packaged into an IPA (iOS App Store Package).An IPA is essentially an archive containing the components required to install and execute the application.2. Anatomy of an IPAA typical IPA contains a structure similar to:Application.ipa │ └── Payload/ │ └── Application.app/ ├── Application ├── Info.plist ├── Frameworks/ ├── PlugIns/ ├── Resources └── Other application files Payload DirectoryThe Payload directory is particularly important during static analysis.It contains the application's .app bundle.Inside the bundle, analysts can locate: Application executable Info.plist Frameworks Resources Embedded components Configuration files 3. Info.plistThe Info.plist file contains important application metadata and configuration information.Depending on the application, it may reveal things such as: Bundle identifier Application version Display name Supported platforms Required capabilities URL schemes Permissions-related configuration Security relevanceDuring static analysis, Info.plist is often one of the first files worth examining because it can provide a quick overview of how the application is configured.4. Application BinaryThe .app bundle normally contains the application's executable binary.For example:Payload/ └── Example.app/ ├── Example ├── Info.plist └── ... The binary contains the compiled application logic.Static AnalysisA basic static-analysis workflow can therefore begin with:IPA ↓ Extract Archive ↓ Open Payload/ ↓ Identify .app Bundle ↓ Inspect Info.plist ↓ Identify Executable ↓ Analyze Binary 🔐 5. The iOS SandboxOne of the most important security mechanisms in iOS is application sandboxing.Each application operates within a restricted environment rather than having unrestricted access to the operating system.Conceptually: iOS │ ┌────────┴────────┐ │ │ App A App B │ │ Sandbox Sandbox │ │ Private Data Private Data The sandbox limits an application's ability to: Access other applications' private data Modify protected system files Interact directly with restricted system resources Escape its designated environment 6. Application ContainersAn application generally has separate areas for different types of data.Conceptually:Application BundleContains the application itself: Executable Resources Configuration Data ContainerContains application-generated data such as: Databases User preferences Cached information Application files Temporary StorageUsed for temporary data that does not need permanent storage.🧪 7. Static Analysis of an IPAA basic analysis begins by extracting the IPA.Conceptually:Application.ipa ↓ Extract ↓ Payload/ ↓ Application.app/ ↓ ┌───────────────┐ │ Info.plist │ │ Executable │ │ Frameworks │ │ Resources │ └───────────────┘ The objective at this stage is to understand: What the application contains What executable it uses What configuration it declares What frameworks and resources are bundled 🔓 8. What Is Jailbreaking?Jailbreaking is the process of circumventing Apple's software restrictions to obtain greater control over an iOS device.A jailbroken device may allow researchers to: Execute software outside normal restrictions Access normally protected areas of the...
Ready to play
Course 42 - Mobile Malware Analysis Fundamentals | Episode 3: iOS Application Architecture and Jailbreaking Fundamentals
No transcript for this episode yet
Similar Episodes
No similar episodes found.