First Sednit UEFI Rootkit Unveiled (35c3)
from Chaos Computer Club - archive feed (high quality) Hosted by Frédéric Vachon
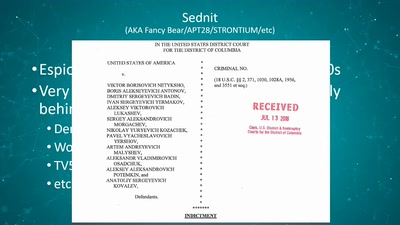
UEFI rootkits have been researched and discussed heavily in the past few years, but sparse evidence has been presented of real campaigns actively trying to compromise systems at this level. Our talk will reveal such a campaign successfully executed by the Sednit group. We will detail the full infection chain showing how Sednit was able to install their custom UEFI module on key targets' computers. Additionally, we will provide an in-depth analysis of their UEFI module and the associated trojanized LoJack agent. UEFI rootkits have been researched and discussed heavily in the past few years, but sparse evidence has been presented of real campaigns actively trying to compromise systems at this level. Our talk will reveal such a campaign successfully executed by the Sednit group. This APT group, also known as Fancy Bear, Sofacy and APT28, has been linked to numerous high profile cyberattacks such as the 2016 Democratic National Committee email leak scandal. Earlier this year, there was a public report stating that the infamous Sednit/Sofacy/APT28 APT group successfully trojanized a userland LoJack agent and used it against their targets. LoJack, an embedded anti-theft application, was scrutinized by security researchers in the past because of its unusual persistence method: a module preinstalled in many computers' UEFI/BIOS software. Over the years, several security risks have been found in this product, but no significant in-the-wild activity was ever reported until the discovery of the Sednit group leveraging some of the vulnerabilities affecting the userland agent. However, through our research, we now know that Sednit did not stop there: they also tried to, and succeeded, in installing a custom UEFI module directly into a system's SPI flash memory. In this talk, we will detail the full infection chain showing how Sednit was able to install their custom UEFI module on key targets' computers. Additionally, we will provide an in-depth analysis of their UEFI module and the associated trojanized LoJack agent. about this event: https://fahrplan.events.ccc.de/congress/2018/Fahrplan/events/9561.html
Embed this episode
No transcript yet.